Cyber Resilience
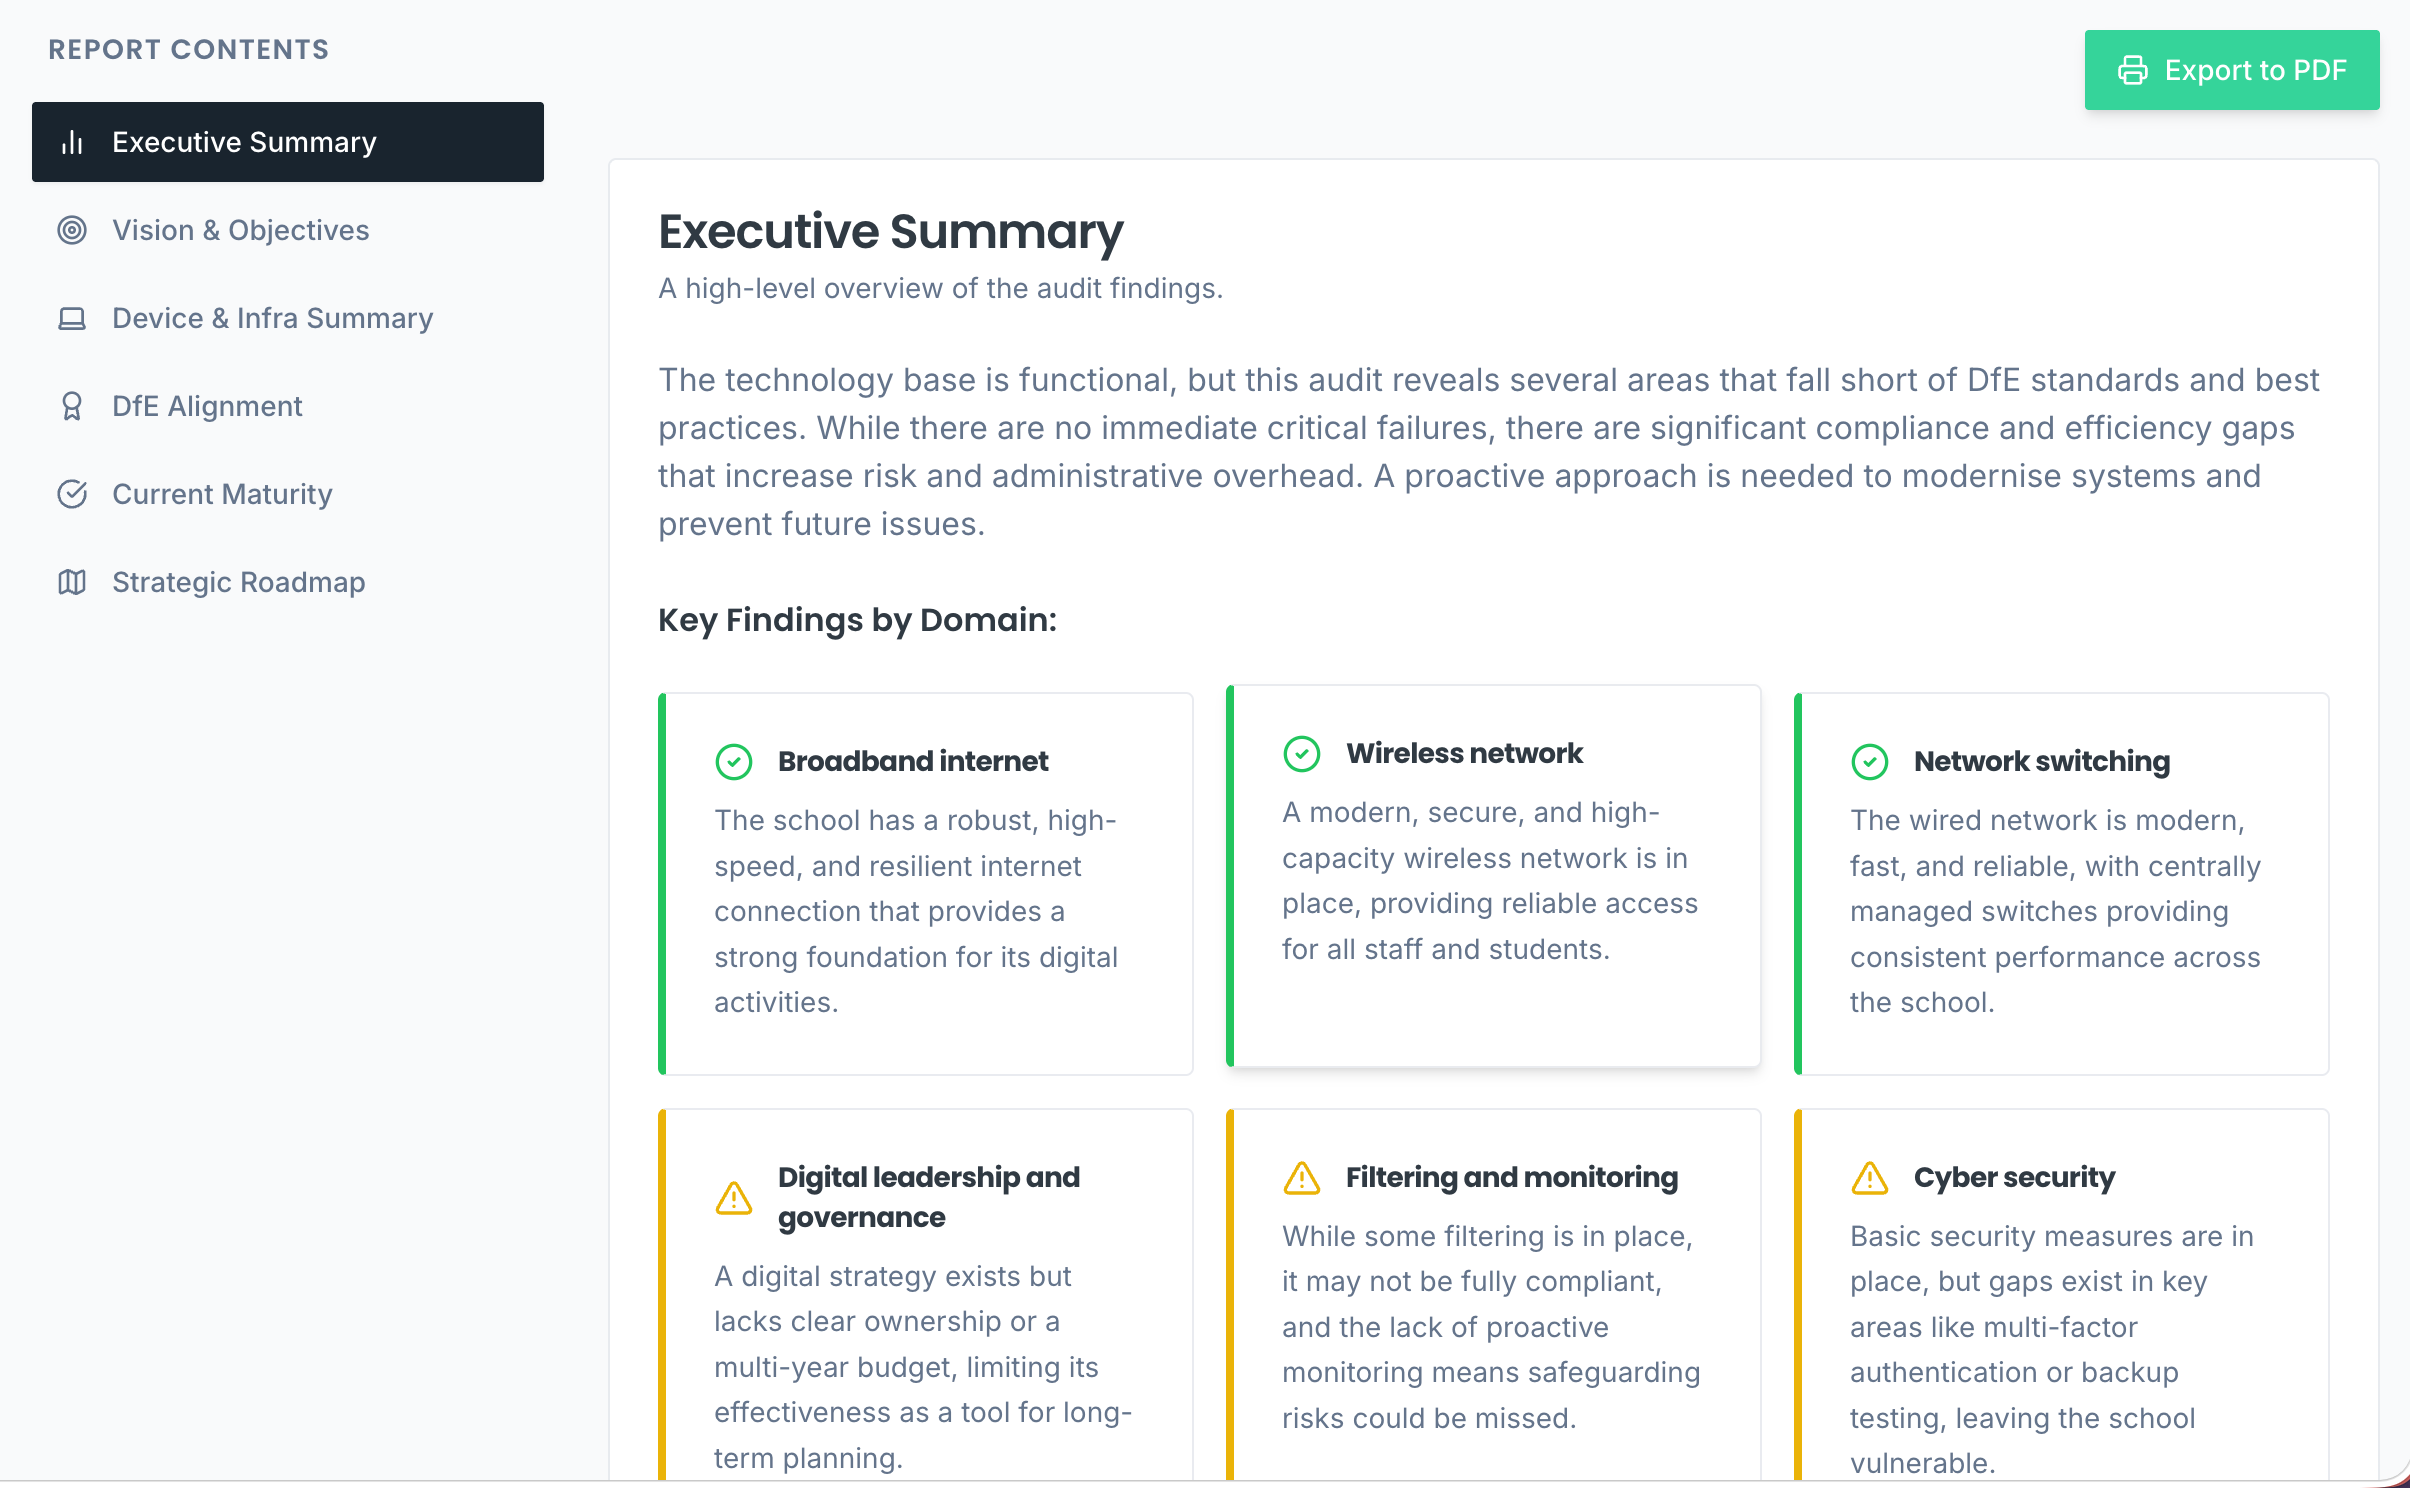
Framework-led security gap analysis
Strategic planning
Costed multi-year IT roadmaps
Asset lifecycle
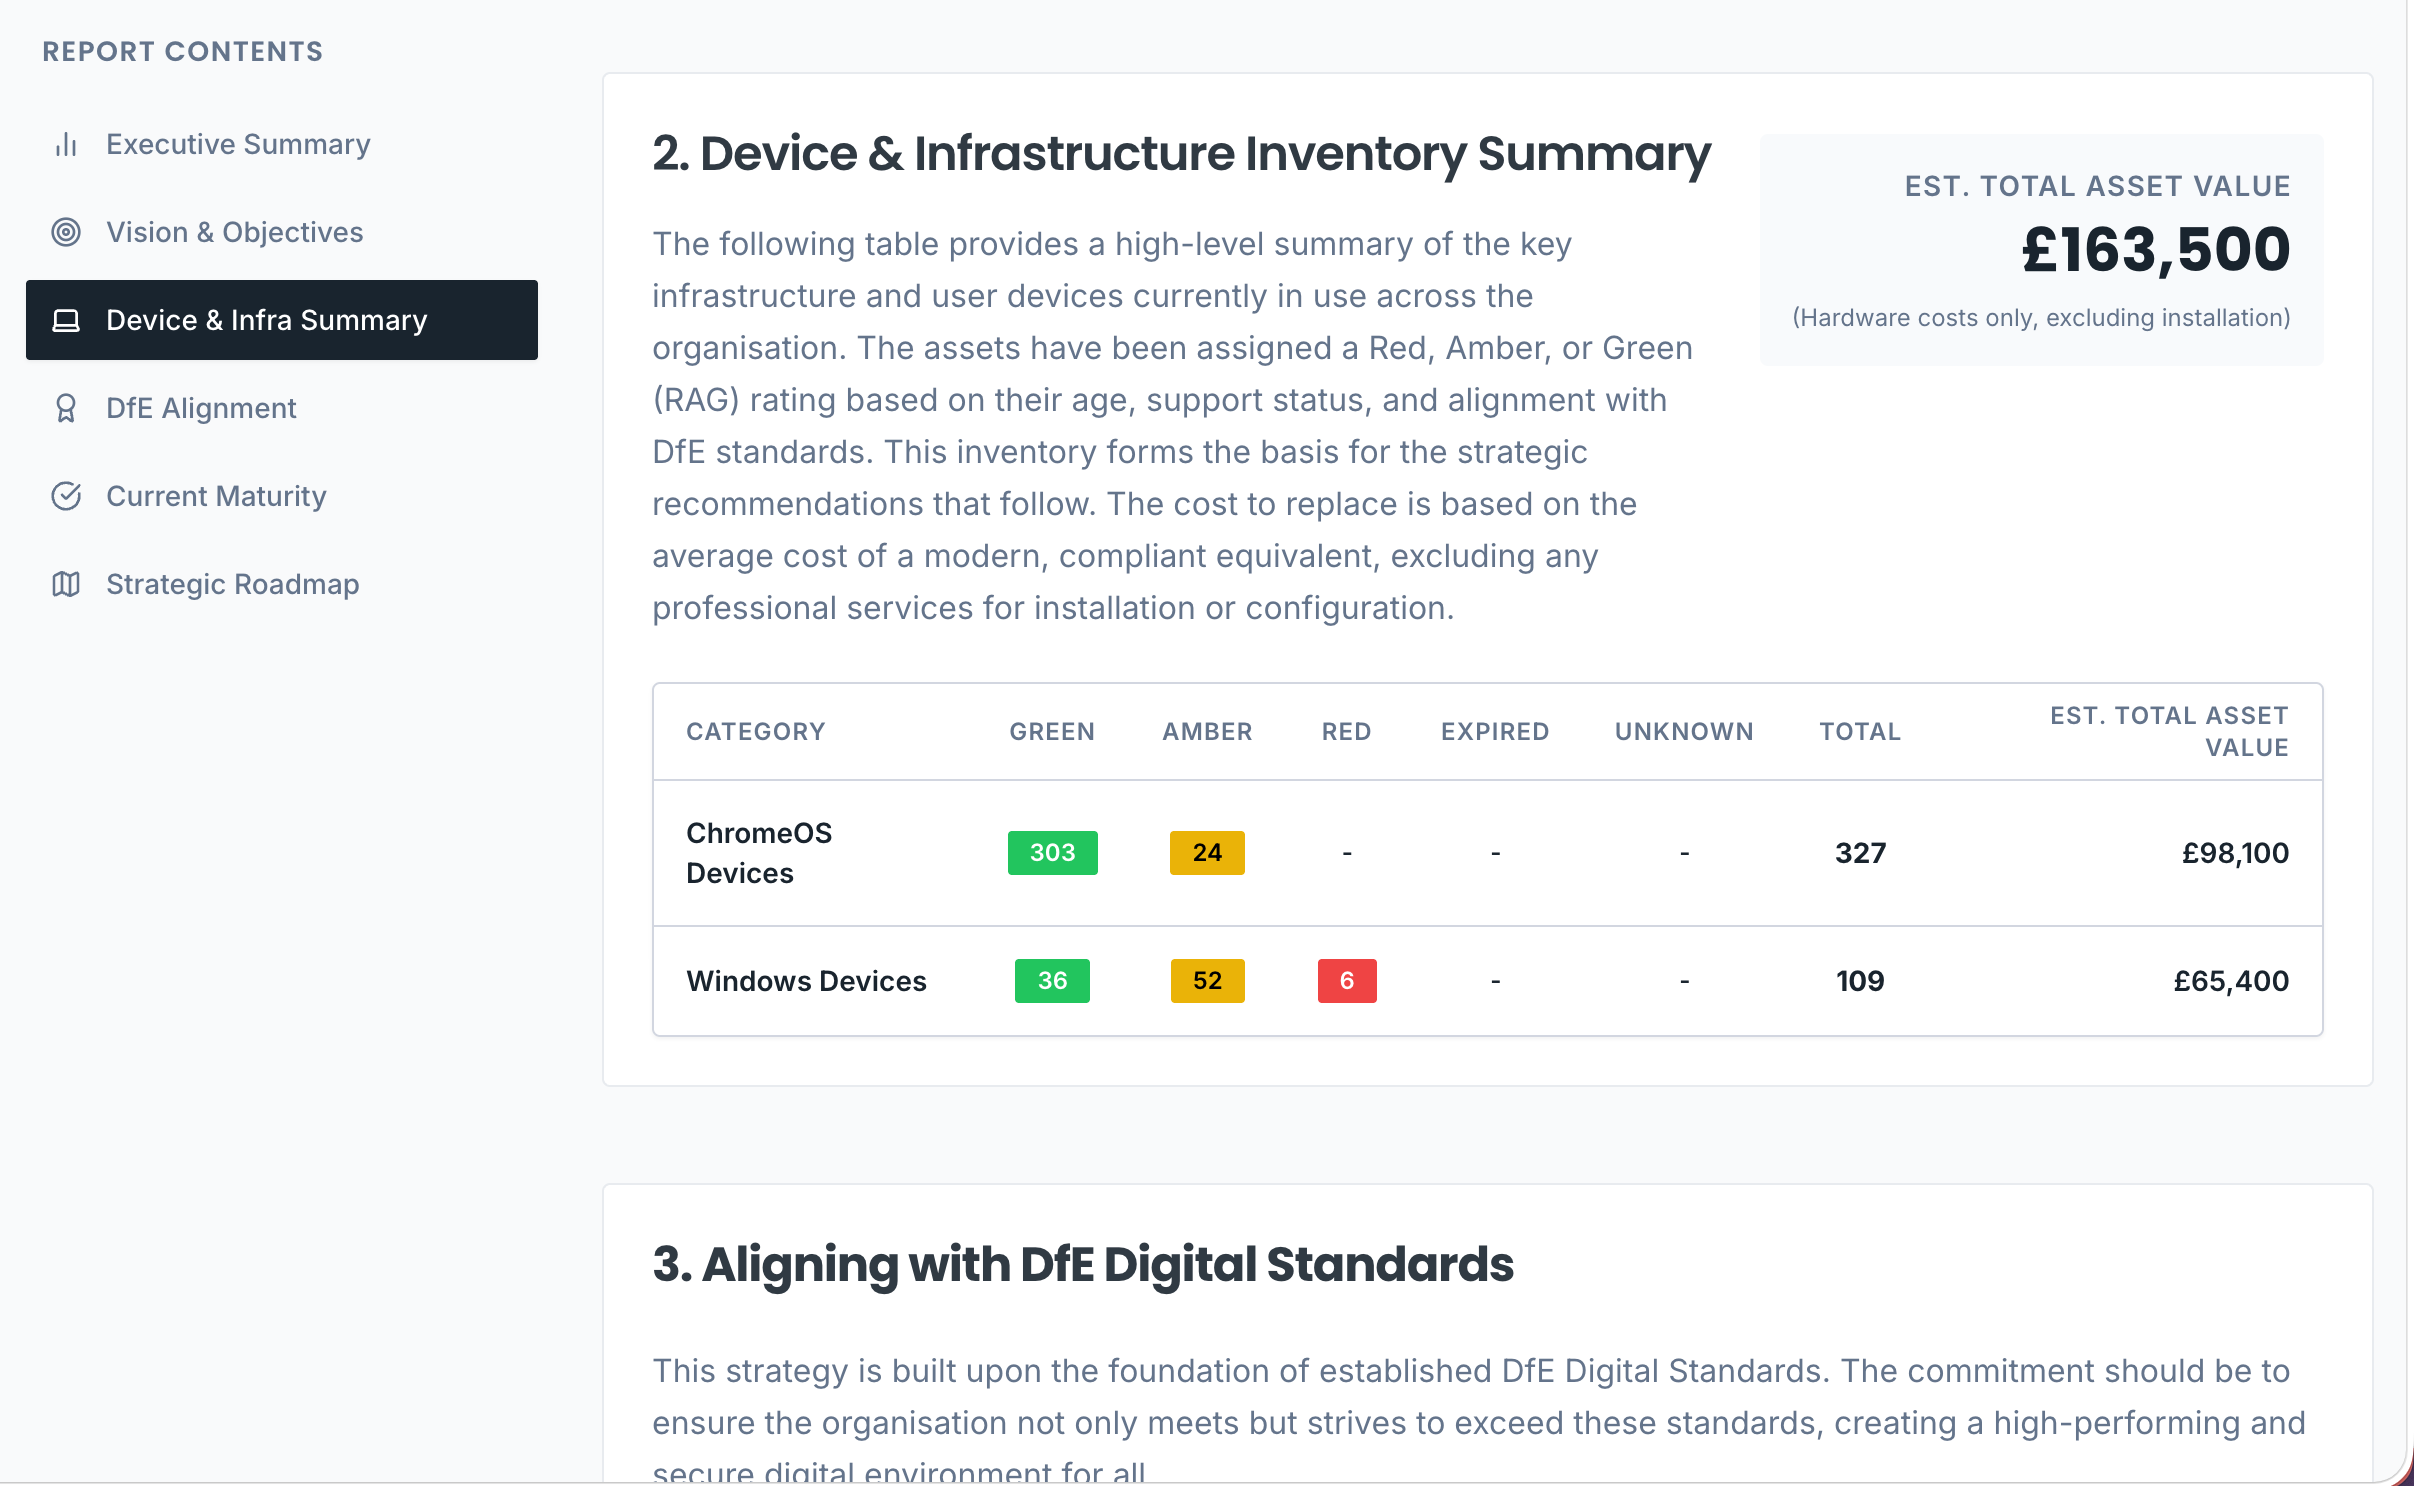
Forecast replacement priorities
Board reporting
Clear, commercial summaries
audit
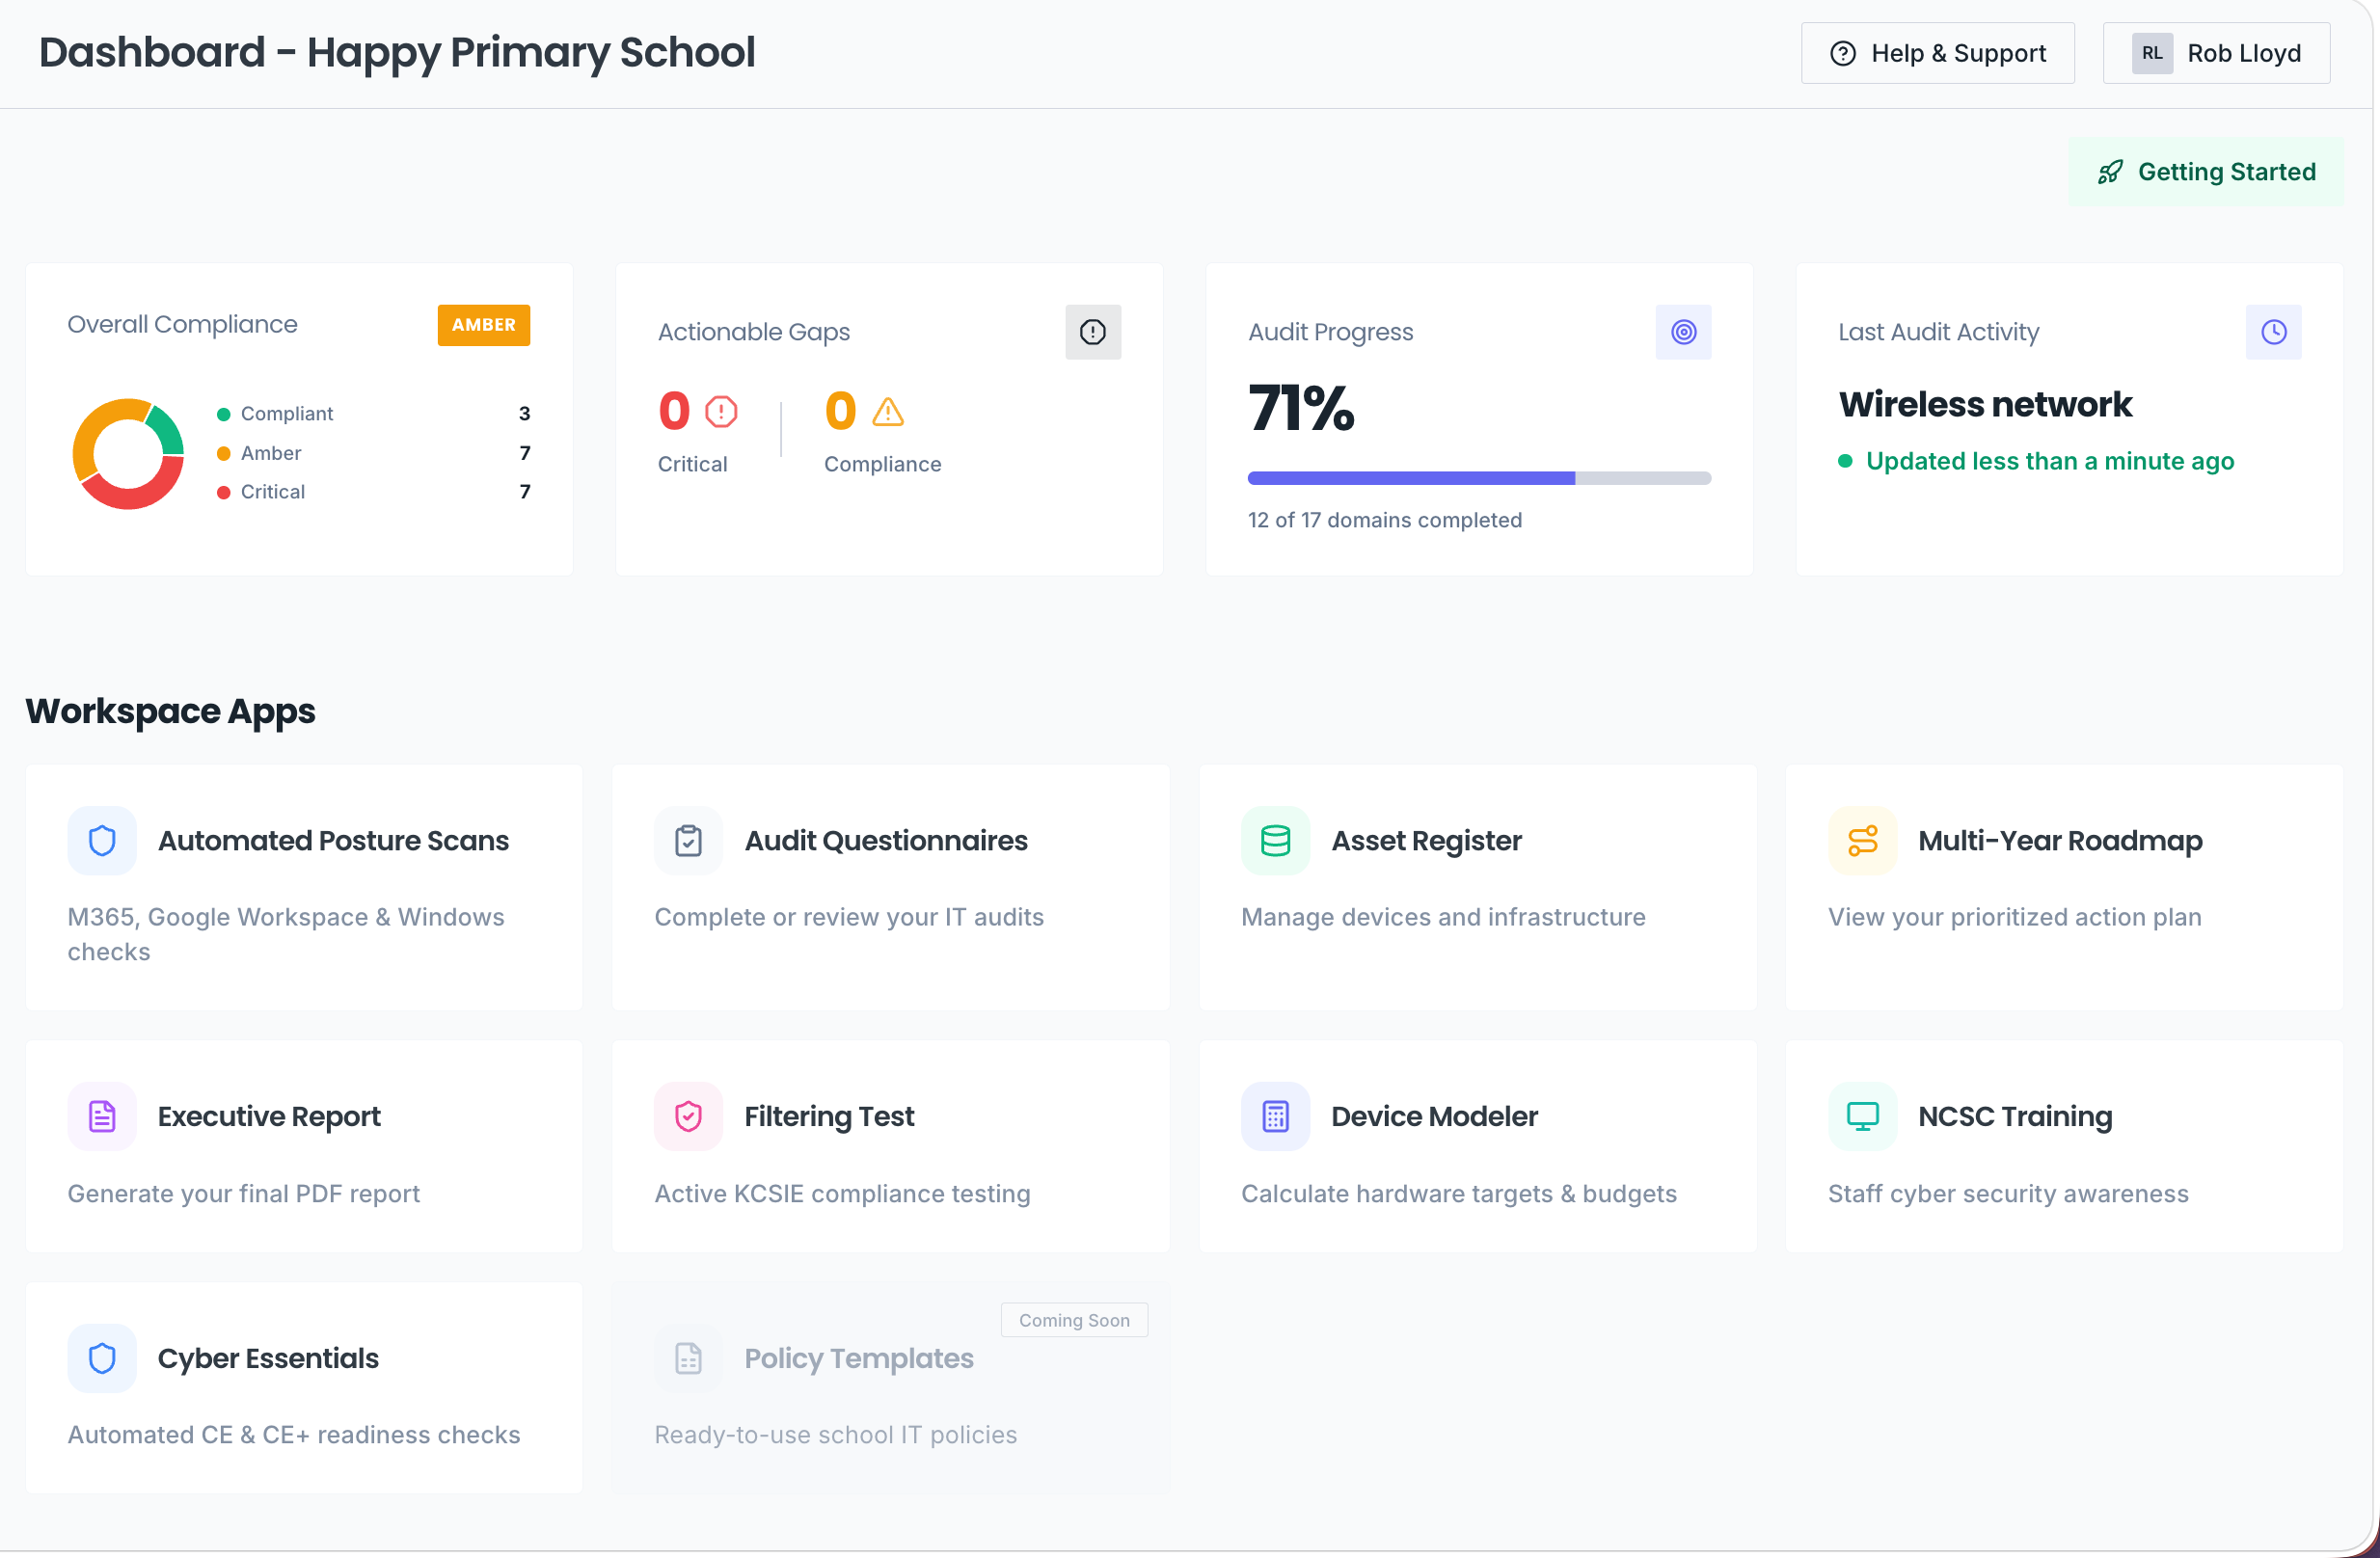
Understand the present
Bring IT assessments, cyber security evidence, asset information and identified risks into one consistent view.
- Consolidate assessment evidence
- Identify standards gaps (Cyber Essentials/ISO)
- Establish the current business baseline
strategise
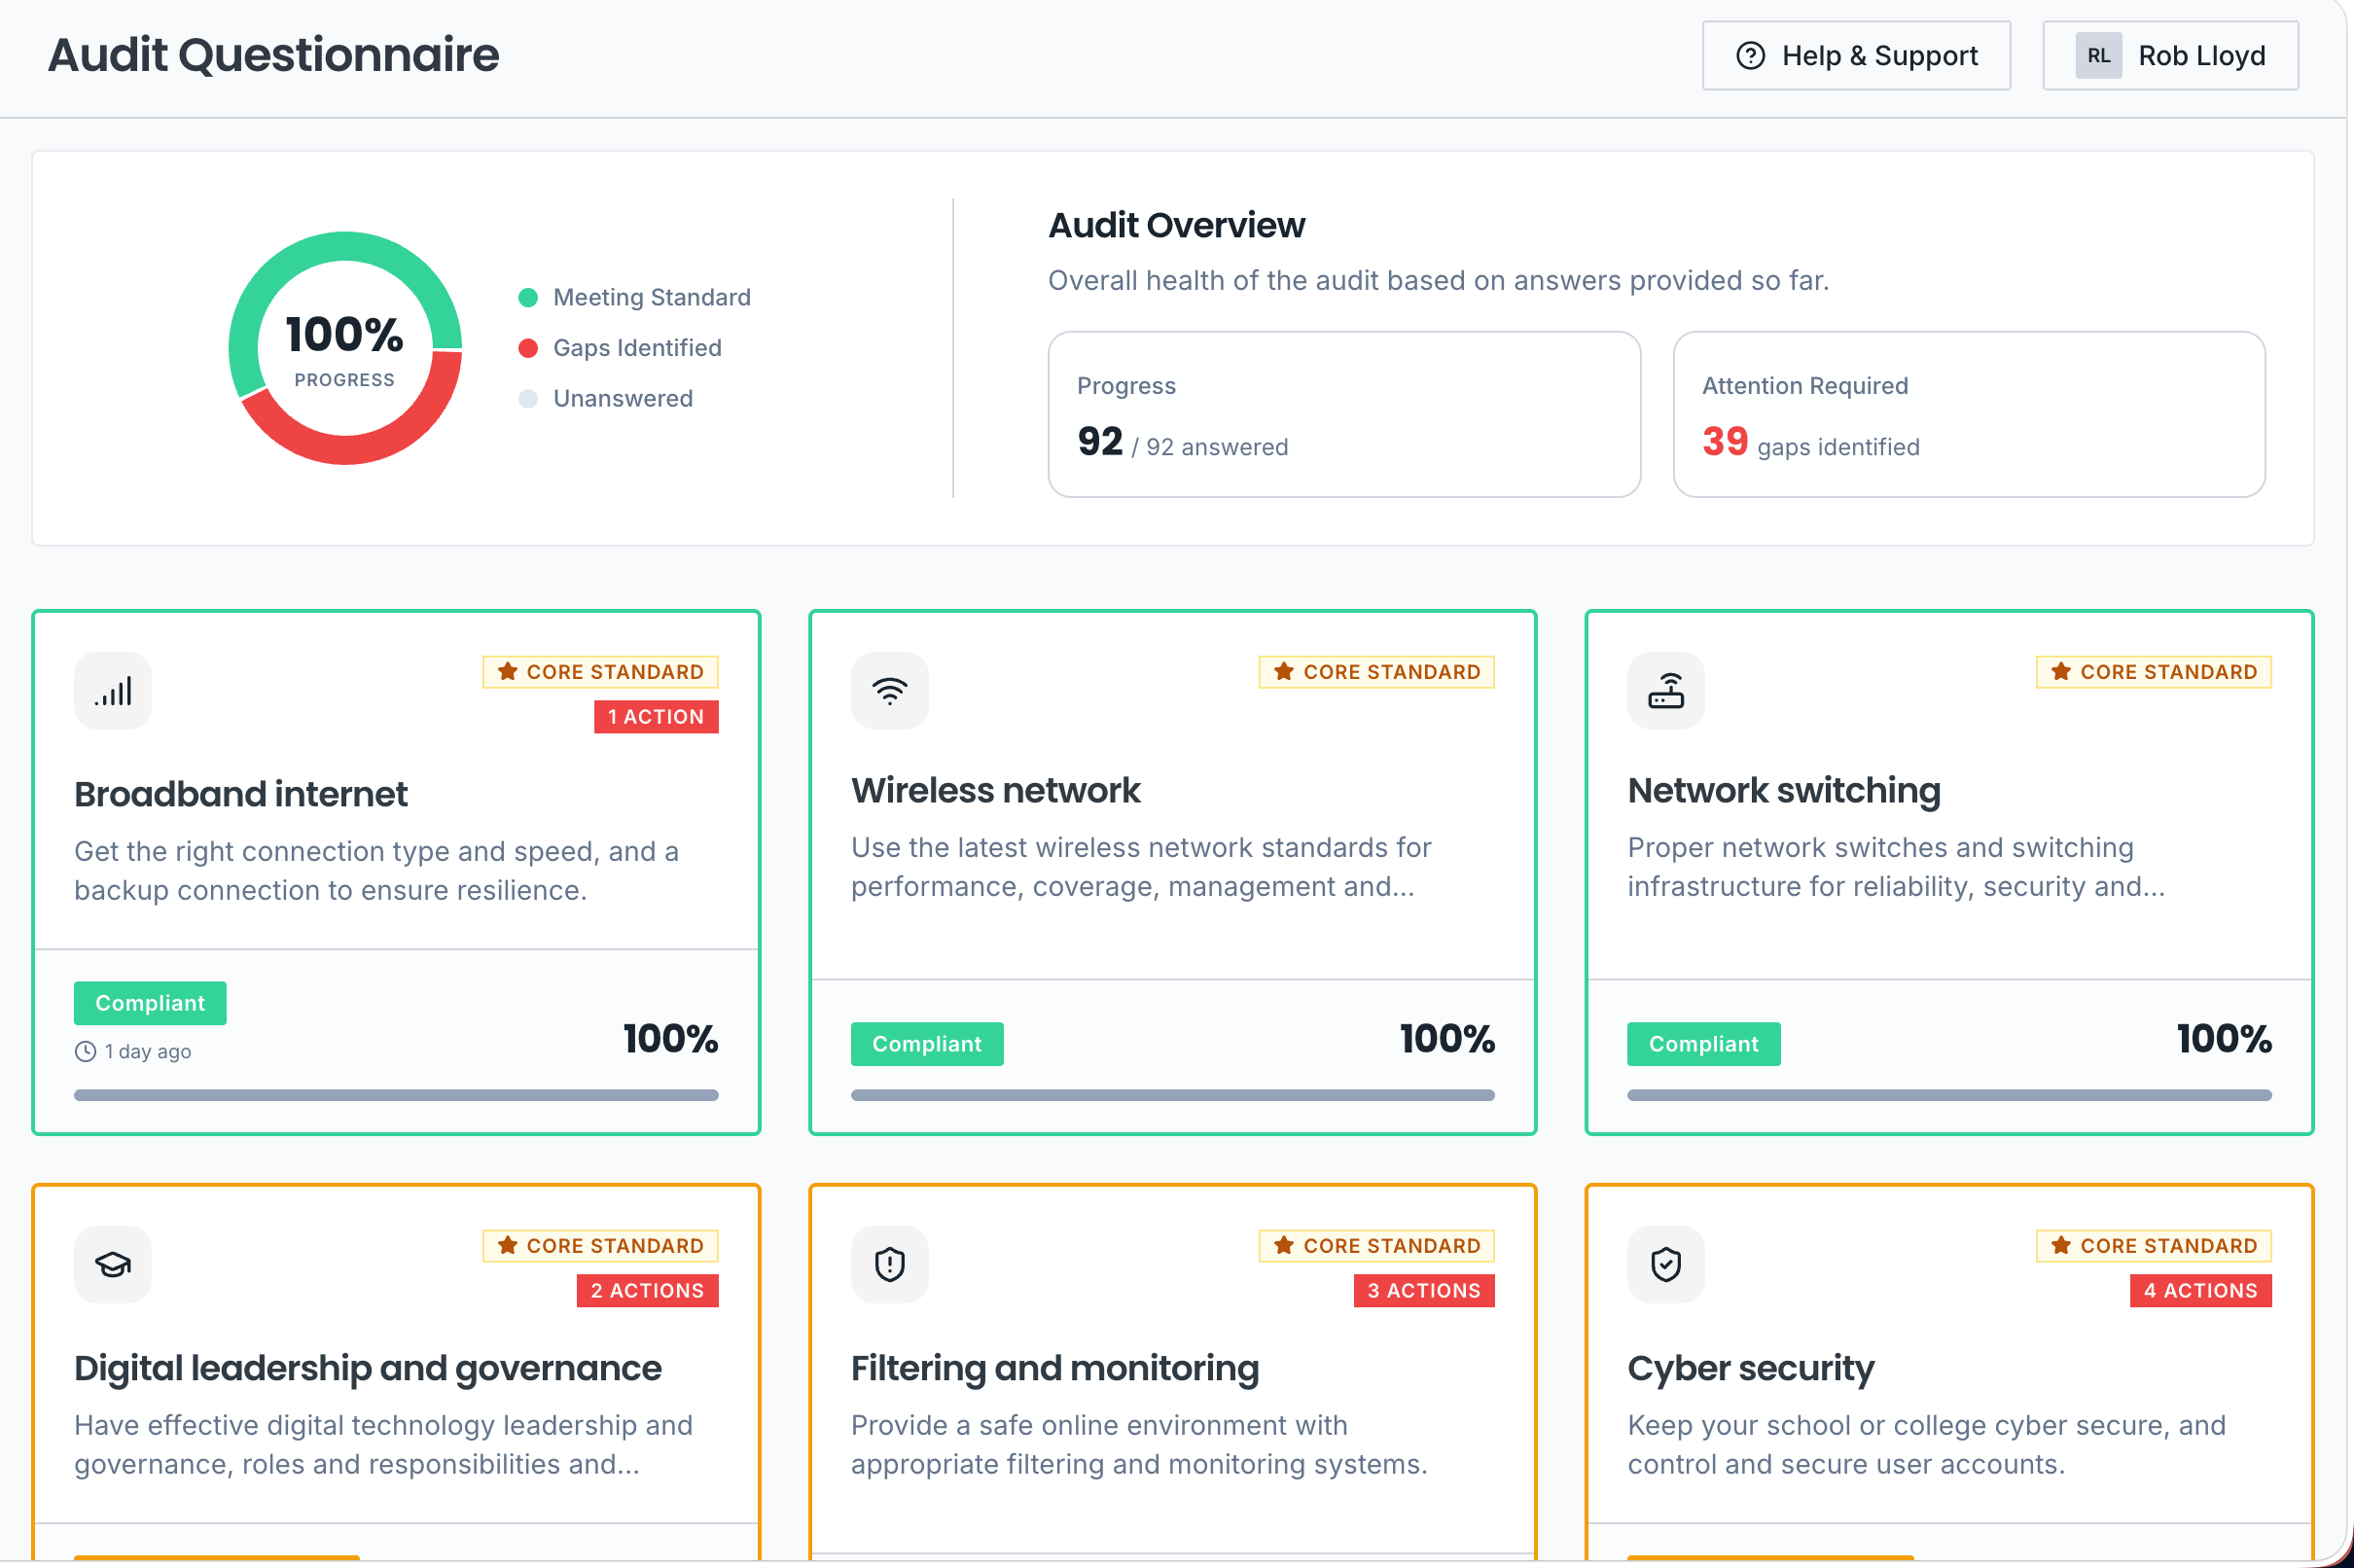
Decide what happens next
Convert findings into commercial priorities, dependencies, lifecycle decisions and costed multi-year plans.
- Prioritise commercial recommendations
- Plan dependencies and costs
- Build a phased roadmap
achieve
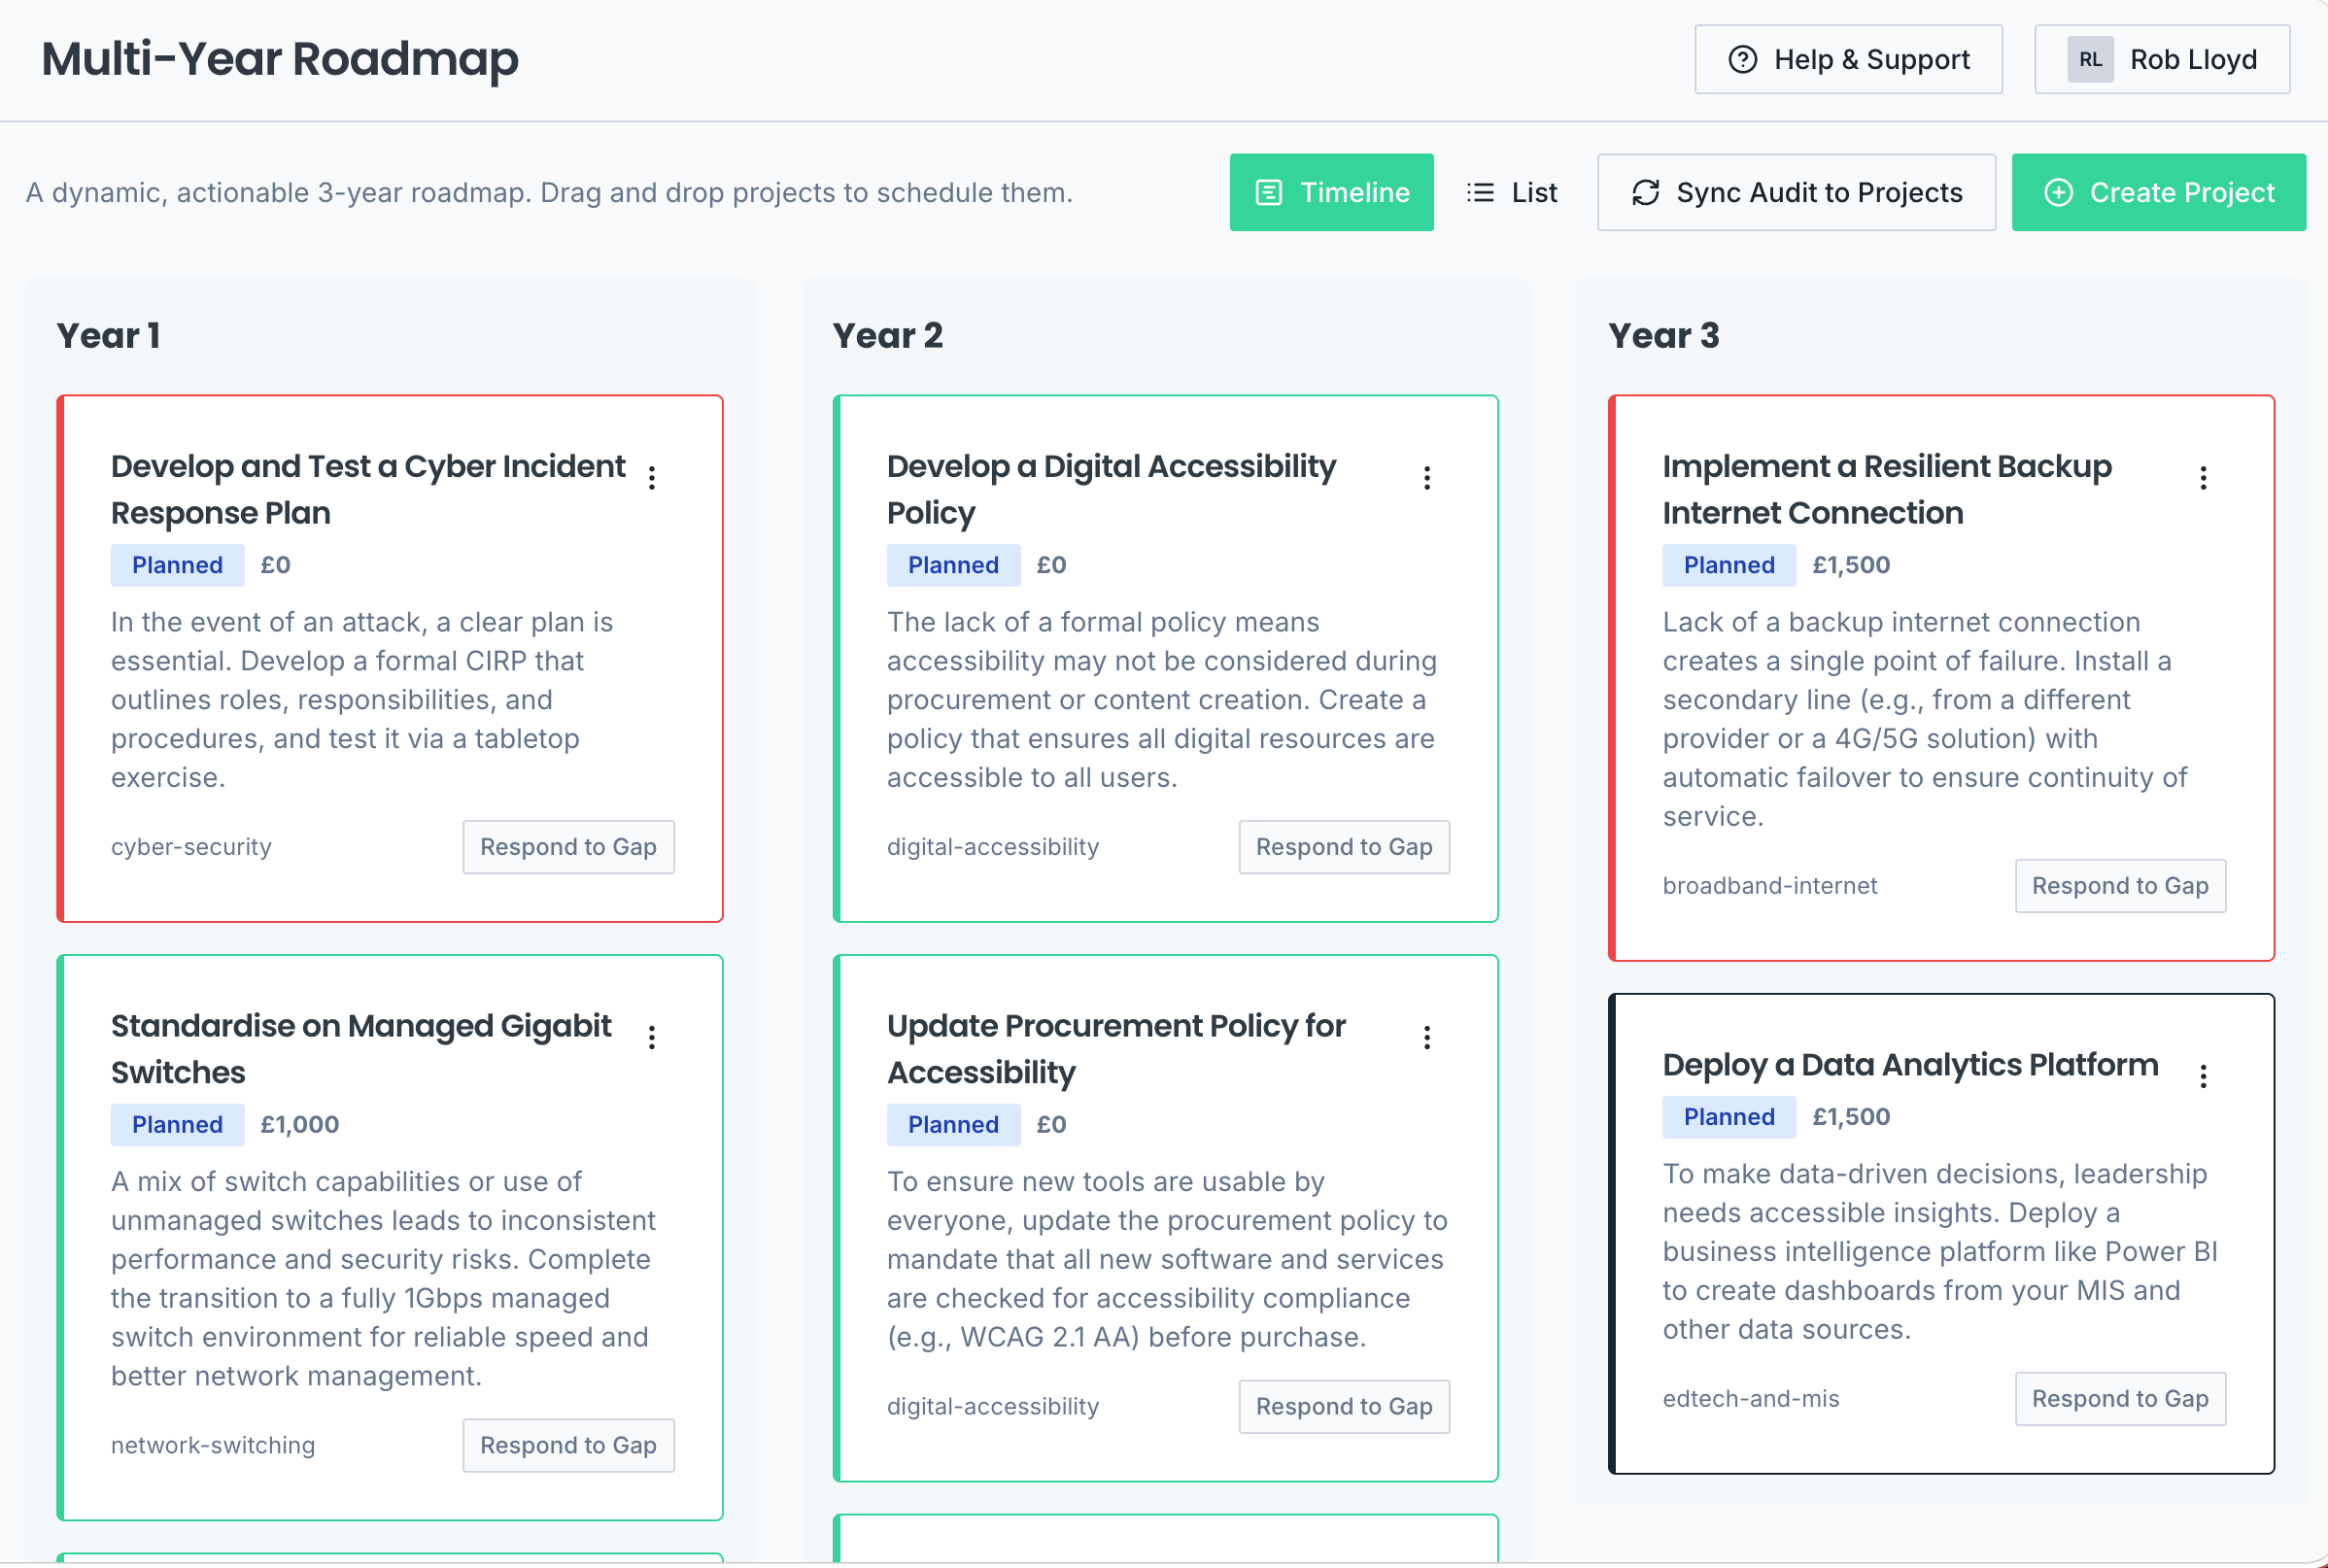
Turn plans into evidenced progress
Structure improvement actions, record progress and evidence, and maintain clear oversight of the roadmap for the Board.
- Assign and monitor actions
- Retain completion evidence
- Report commercial progress clearly
Built for Business
Choose how you use asitplan within your organisation.
Business Leaders
Understand risk and defend investment
See current technology risks, financial implications and a clear roadmap for the board.
IT Managers
Replace fragmented evidence
Bring audit findings, asset information and planning data into one structured baseline mapped to standard frameworks.
Finance Directors
Connect decisions to cost
Identify commercial risk, forecast hardware replacement, and build an achievable Opex/Capex plan.